POPULAR COURSES
Master Programs
Table of contents:
|
1. Industry Certifications: Structuring Your Learning Pathway
|
|
2. Essential Tools & Hands-On Skills Mastery
|
|
3. Cybersecurity Roles, Salary Insights & Market Growth
|
|
4. Cross-Role Skill & Salary Matrix |
|
5. Why Choose Apponix Technologies for Your Cybersecurity Journey? |
|
6. Conclusion |
Building a successful ethical hacking career has become one of the most resilient and high-growth professional trajectories in technology.
Enrolling with a top-rated Training institute in Bangalore equips aspiring security engineers with the practical offensive security skills, hands-on lab experience, and industry-aligned knowledge required to defend modern enterprise infrastructures.
According to IBM's Cost of a Data Breach Report, the average cost of an enterprise data breach in India reached an all-time high of ₹25.5 crore, representing a 15.9% year-over-year increase. At the same time, reports from the Data Security Council of India (DSCI) and industry analysts highlight a severe talent shortage, with demand for skilled cybersecurity specialists outstripping supply by over 30% to 40% across enterprise risk, threat intelligence, and cloud security domains.
As organizations rapidly adopt cloud architectures, agentic AI tools, and digital financial platforms, white-hat hackers are no longer optional additions to IT departments; they are vital line-of-defense assets. Offensive security assessments, including systematic vulnerability scanning and proactive red teaming, allow businesses to identify critical system flaws before malicious threat actors exploit them.
This guide provides a comprehensive roadmap detailing key industry certifications, essential tools, and regional salary benchmarks to help you launch a rewarding career in cybersecurity.
Industry Certifications: Structuring Your Learning Pathway
Industry certifications act as standardized benchmarks that validate your theoretical knowledge, hands-on methodology, and problem-solving abilities under simulated attack scenarios.
For hiring managers across IT service firms, Global Capability Centers (GCCs), and boutique security consultancies, obtaining recognized credentials demonstrates that a candidate possesses verified technical capabilities.
Navigating the cybersecurity certification landscape requires selecting credentials that align with your experience level and career trajectory.
Key Industry Certifications Comparison
|
Certification |
Certifying Body |
Exam Structure & Duration |
Difficulty & Prerequisites |
Primary Focus Area
|
|---|---|---|---|---|
|
Certified Ethical Hacker (CEH v13) |
EC-Council |
125 Multiple-Choice Questions (4 Hours) + Optional 6-Hour Practical Exam |
Beginner to Intermediate (2 years IT/security experience recommended) |
Core methodology, threat vectors, AI-driven hacking tools, and compliance frameworks. |
|
CompTIA PenTest+ |
CompTIA |
Up to 85 Performance-Based & Multiple-Choice Questions (165 Minutes) |
Intermediate (3–4 years of hands-on security experience recommended) |
Vulnerability management, scope compliance, and web application exploitation. |
|
Offensive Security Certified Professional (OSCP) |
OffSec |
24-Hour Hands-On Practical Exam + 24-Hour Technical Report |
Advanced (Deep Linux, networking, and manual exploitation required) |
Penetration testing, Active Directory exploitation, and privilege escalation. |
Navigating the Certification Tier List
-
Certified Ethical Hacker (CEH v13): Recognized globally as an entry-to-intermediate standard, EC-Council's curriculum covers the 20 most critical security domains, including malware analysis, social engineering, wireless security, and cloud threat vectors. Obtaining a CEH certification demonstrates foundational competency across both theoretical concepts and practical attack tools, making it a frequent prerequisite for enterprise HR screening filters.
-
CompTIA PenTest+: This vendor-neutral credential focuses heavily on hands-on, performance-based questions. Candidates must demonstrate proficiency in planning and scoping assessments, performing network reconnaissance, evaluating legal compliance constraints, and documenting vulnerability findings for executive stakeholders.
-
Offensive Security Certified Professional (OSCP): Widely considered the gold standard for dedicated red teamers and penetration testers, the OSCP requires passing a grueling 24-hour hands-on practical exam. Candidates are placed in an isolated network environment with no multiple-choice questions and must compromise multiple target machines, escalate privileges, and submit a detailed technical report.
Enrolling in a structured Penetration testing course provides access to guided virtual labs, step-by-step methodology coaching, and instructor mentorship needed to master these complex exam domains. Combining structured training with practical lab practice ensures you build the technical confidence required to earn top-tier industry credentials.
Essential Tools & Hands-On Skills Mastery
Mastering offensive security requires practical, hands-on experience using industry-standard utilities across real-world target environments.
Security engineers utilize specialized ethical hacking tools to conduct systematic reconnaissance, intercept web application traffic, evaluate Active Directory configurations, and simulate real-world cyberattacks in authorized environments.
Understanding how to navigate these security platforms transforms theoretical knowledge into actionable penetration testing skills.
Core Offensive Security Toolkit
-
Nmap (Network Mapper): Considered the fundamental reconnaissance tool for every security practitioner, Nmap conducts host discovery, port scanning, and service version detection. Penetration testers use the Nmap Scripting Engine (NSE) to identify misconfigured network assets, unpatched software versions, and active network vulnerabilities.
-
Burp Suite: The industry-standard web proxy for evaluating web application security. Burp Suite acts as an intercepting proxy between the web browser and target web servers, enabling testers to inspect HTTP/HTTPS traffic, modify request headers, and identify critical web flaws such as SQL injection, Cross-Site Scripting (XSS), and broken access controls.
-
Metasploit Framework: A powerful penetration testing framework used for vulnerability validation and exploit development. Metasploit contains thousands of pre-configured exploit modules and payloads, allowing security analysts to demonstrate the real-world operational impact of unpatched system vulnerabilities.
-
Wireshark: A deep-packet network protocol analyzer used to inspect live network traffic at a microscopic level. Wireshark helps security analysts troubleshoot network communication issues, analyze unencrypted protocol credentials, and detect suspicious data exfiltration activities across local area networks.
-
BloodHound: An Active Directory visualization tool that maps complex domain relationships, trust paths, and permission structures. Red teams utilize BloodHound to identify non-obvious attack paths and execute privilege escalation across enterprise Windows domain environments.
Operating Systems & Virtual Lab Environments
Proficiency in specialized security operating systems is essential for managing offensive toolsets effectively.
Enrolling in structured Kali Linux training teaches security professionals how to leverage Debian-based security distributions pre-configured with over 600 penetration testing tools, eliminating software dependency issues during live assessments.
Practicing in legal, hands-on cyber ranges such as Hack The Box, TryHackMe, and local Virtual Private Cloud (VPC) lab environments allows aspiring ethical hackers to sharpen their exploitation skills safely while building a verifiable portfolio of completed machine write-ups and bug bounty disclosures.
Cybersecurity Roles, Salary Insights & Market Growth
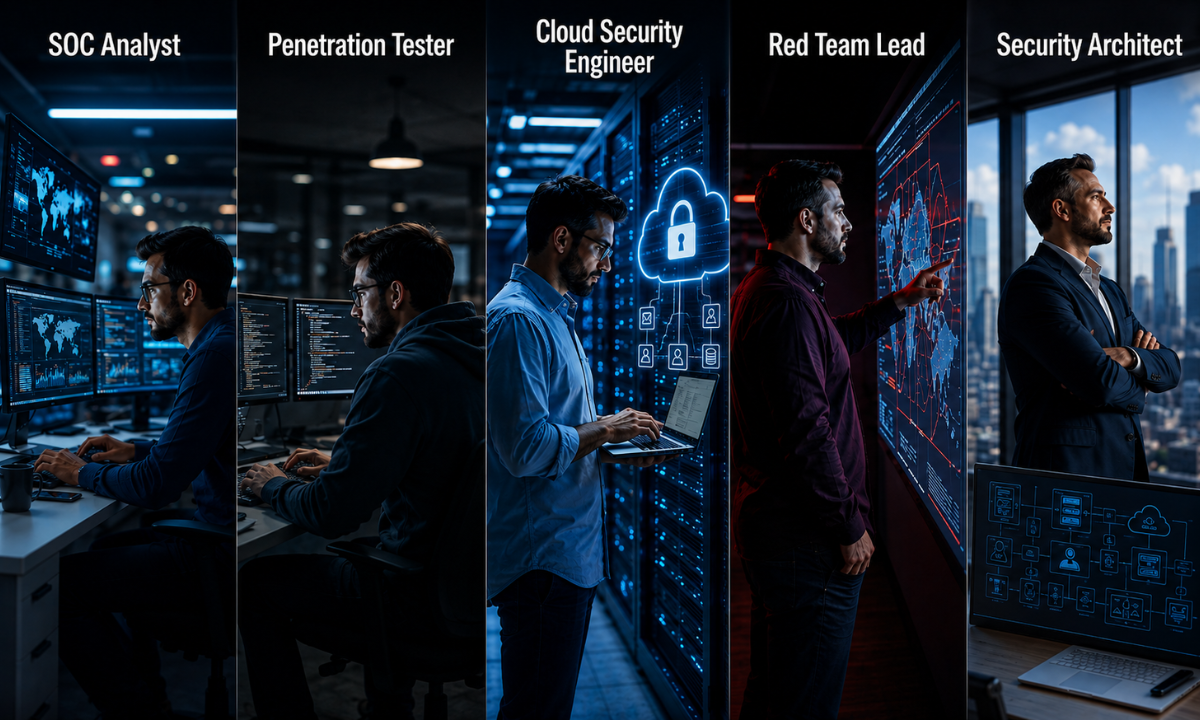
The expansion of digital banking networks, cloud infrastructure, and enterprise SaaS platforms has created diverse career pathways within offensive and defensive cybersecurity.
As organizations transition from reactive incident response to proactive security engineering, specialized roles command significant compensation premiums across major Indian tech hubs like Bengaluru, Hyderabad, and NCR.
Core Cybersecurity Roles & Responsibilities
-
Vulnerability Assessment & Security Analyst (SOC): Entry-level security professionals who monitor Security Information and Event Management (SIEM) dashboards, analyze alert streams, and execute routine vulnerability scans across enterprise networks.
-
Penetration Tester / Red Team Specialist: Offensive specialists who simulate real-world cyberattacks against web applications, mobile platforms, Active Directory environments, and wireless networks to identify exploitable security weaknesses before malicious actors do.
-
Cloud & DevSecOps Engineer: Security engineers who embed automated security checks, static code analysis (SAST), and dynamic security testing (DAST) directly into CI/CD build pipelines and cloud infrastructure configurations.
-
Security Architect / CISO: Senior leadership professionals responsible for designing enterprise-wide zero-trust security frameworks, overseeing regulatory compliance, and managing organizational risk posture.
Salary Insights Across Experience Levels in India
Compensation in the Indian cybersecurity sector scales rapidly with hands-on technical proficiency, specialized domain expertise, and practical lab capabilities.
|
Experience Level |
Typical Industry Roles |
Average Annual Package (INR)
|
|---|---|---|
|
Fresher (0–1 Year) |
Associate SOC Analyst, Junior Vulnerability Tester |
₹4.5 LPA – ₹6.5 LPA |
|
Mid-Level (2–5 Years) |
Penetration Tester, Security Engineer, DevSecOps Analyst |
₹8.0 LPA – ₹16.0 LPA |
|
Senior (6–10+ Years) |
Red Team Lead, Principal Security Architect, CISO |
₹22.0 LPA – ₹45.0+ LPA |
Earning an industry-recognized Network security certification enables infrastructure administrators and systems engineers to prove fundamental security management skills, facilitating a smooth career transition into specialized threat analyst and penetration testing roles.
Regional Market Demand & Growth Trajectory
Tech hubs like Bengaluru lead the national average in cybersecurity compensation, driven by the concentration of Global Capability Centers (GCCs), FinTech unicorns, and multinational product engineering firms.
Professionals who combine practical offensive testing skills with strong scripting capabilities (in Python, Bash, or PowerShell) and cloud security knowledge routinely command 30% to 50% higher compensation packages compared to general IT roles.
Cross-Role Skill & Salary Matrix
Matching your technical domain interests with industry-standard toolsets, certification benchmarks, and compensation expectations allows you to chart a clear career path in cybersecurity.
The matrix below outlines primary job roles across Indian tech hubs, highlighting how specialized certifications and hands-on tool proficiencies directly influence earning potential.
|
Job Role / Specialization |
Primary Core Tools & Tech Stack |
Recommended Certifications |
Average India Salary Band (LPA)
|
|---|---|---|---|
|
Vulnerability Analyst / SOC Analyst |
Wireshark, Nmap, Splunk, Nessus, QRadar |
CompTIA Security+, CEH, Cisco CyberOps |
₹4.5 LPA – ₹8.5 LPA |
|
Penetration Tester (Web / Mobile / Network) |
Burp Suite, Metasploit, Kali Linux, OWASP ZAP, MobSF |
CEH Practical, CompTIA PenTest+, OSCP |
₹7.0 LPA – ₹16.0 LPA |
|
DevSecOps & Cloud Security Engineer |
AWS Security Hub, Docker, SonarQube, Terraform, Trivy |
AWS Security Specialty, CCSP, Certified Kubernetes Security Specialist (CKS) |
₹10.0 LPA – ₹22.0 LPA |
|
Red Team Specialist / Lead |
BloodHound, Cobalt Strike, Empire, Mimikatz, Python/PowerShell |
OSCP, OSEP, CRTO (Certified Red Team Operator) |
₹18.0 LPA – ₹32.0+ LPA |
|
Security Architect / CISO |
Enterprise Architecture Frameworks, NIST, ISO 27001, SIEM/XDR |
CISSP, CISM, CISA |
₹25.0 LPA – ₹50.0+ LPA |
Note: Tech hubs like Bengaluru, Hyderabad, and NCR command a 15% to 25% salary premium over national base rates due to the high density of Global Capability Centers (GCCs), FinTech firms, and product engineering teams.
Why Choose Apponix Technologies for Your Cybersecurity Journey?
Enrolling in a comprehensive Ethical Hacking course in Bangalore at Apponix Technologies provides the structured mentorship, live cyber-range access, and hands-on tool practice required to transition from theoretical cybersecurity concepts to enterprise-level threat assessment.
Self-study and isolated online tutorials can introduce basic concepts, but mastering professional vulnerability analysis, web application exploitation, and enterprise network defense requires guided instruction from active industry security leads.
Apponix offers a practical, job-oriented training experience designed to prepare you for high-demand cybersecurity roles:
-
40+ Hours of Practical Cyber-Range Labs: Gain hands-on experience executing network scans, web application penetration tests, and wireless security audits in dedicated virtual laboratory environments.
-
EC-Council & Industry Certification Assistance: Receive structured exam preparation support, practice questions, and lab guidance tailored for credentials like CEH.
-
1-on-1 Resume Engineering & Portfolio Building: Optimize your professional resume to highlight practical lab write-ups, vulnerability disclosures, and hands-on penetration testing methodologies to clear ATS screening filters.
-
Mock Technical Interviews & Attack Scenario Simulations: Practice whiteboarding attack methodologies, explaining vulnerability remediation steps, and answering scenario-based interview questions under realistic evaluation conditions.
-
Direct Placement Connections Across Bangalore Tech Parks: Leverage Apponix's established recruitment network across major Bangalore IT hubs and Global Capability Centers for guaranteed interview opportunities.
Combining practical lab execution with personalized mentorship and dedicated placement support, Apponix empowers aspiring security engineers to build verifiable technical skills and step confidently into high-paying cybersecurity roles.
Conclusion
Launching a successful career in offensive security requires a disciplined, practical approach centered on continuous skill development. Start by mastering networking fundamentals, operating systems, and core security principles before progressing to hands-on tool applications. Dedicate regular hours to practicing in legal virtual cyber ranges, building a public portfolio of machine write-ups, and participating in authorized bug bounty programs to demonstrate real-world problem-solving capabilities.
Complement your practical exercises with structured certification preparation to validate your skills for enterprise recruiters. By pairing rigorous hands-on practice with specialized training and active networking across Bangalore's thriving technology ecosystem, you position yourself to capture high-growth opportunities and protect critical digital infrastructure against evolving cyber threats.
Reference:
1. https://www.icertglobal.com/blog/ethical-hacking-salary-2026-guide
2. https://www.collegesimplified.in/post/ethical-hacking-career-guide-2026-skills-salary-certifications-complete-roadmap

Apponix Academy
Apponix Academy